# RBAC setup to use Graph Service in Service Suite
RBAC (Role-Based Access Control) for applications will eventually replace application access policies (see below). Today, the public preview shows some ragged edges in terms of the integration between Exchange Online and Azure AD that Microsoft says they’ll fix before general availability. Even with some bumps to navigate, the new functionality is a welcome addition that extends tenant control over their data, which is always a good thing.
In order to use this protocol you need to do the following configurations in your azure account so the roles and permissions are set correctly.
Once you have done the below steps you should be able to use the service suite Graph Service oauth2 client to send/receive emails using RBAC with the normal client commands.
1. Open Windows PowerShell as an Administrator
2. Execute: `connect-mggraph -scopes "Application.Read.All"`. If the exception *"The term connect-mggraph' is not recognized as the name of a cmdlet"* appears, execute the command
`install-module microsoft.graph`
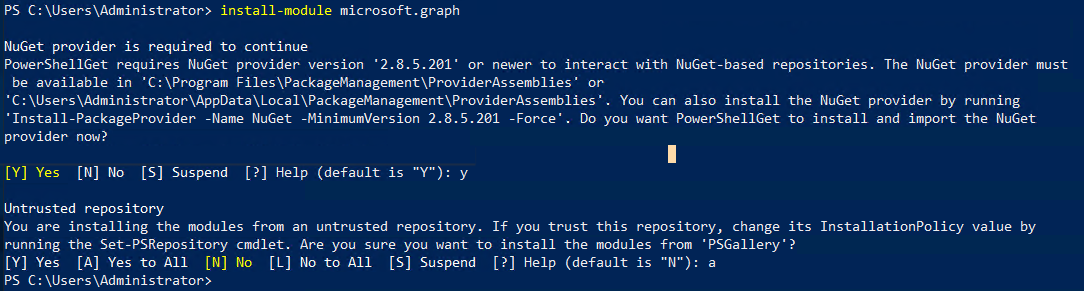
3. After Microsoft Graph is installed, execute again the command `connect-mggraph -scopes "Application.Read.All"`
4. Sign in
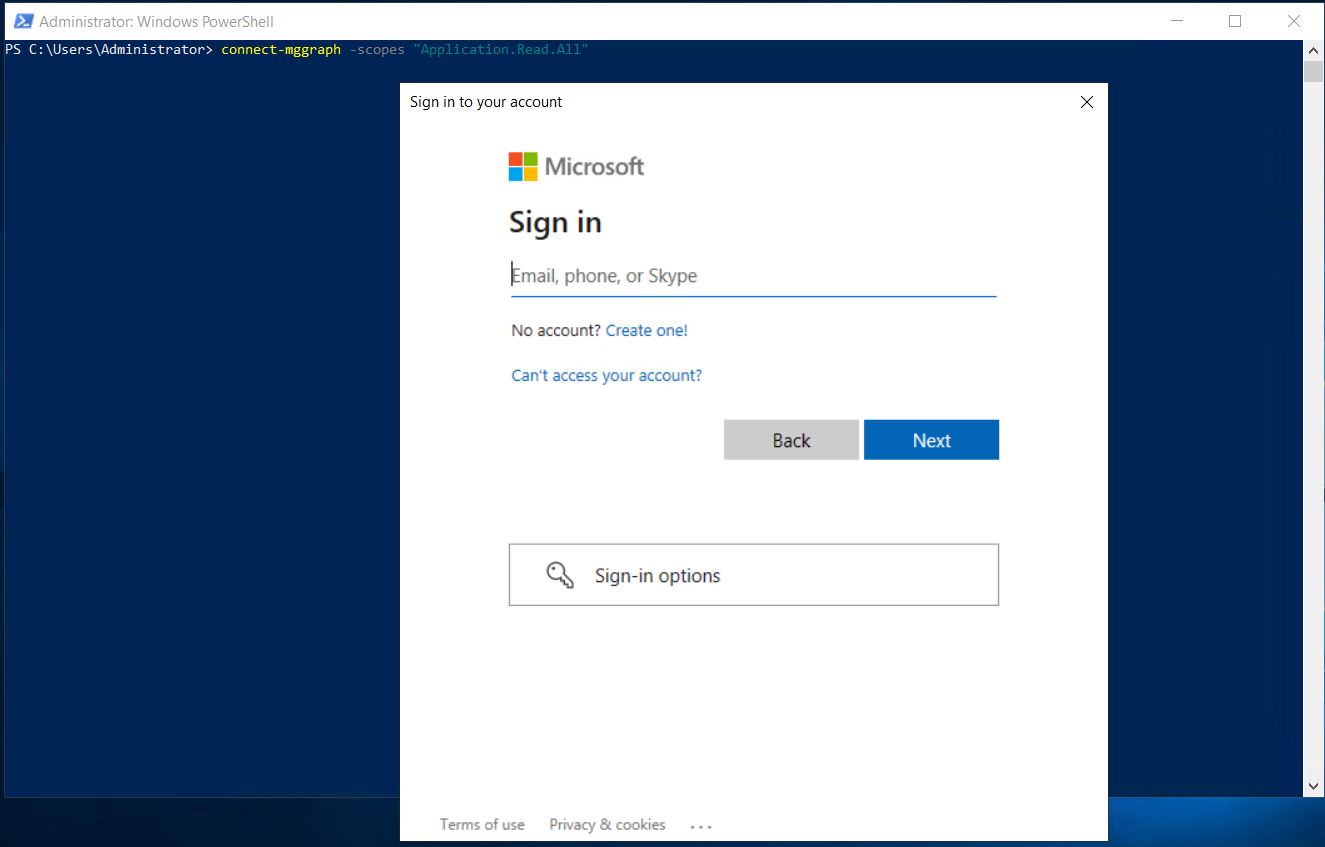
5. After signing in, should see this:

6. Execute: `$SP = Get-MgServicePrincipal -All`
7. Execute: `$ServicePrincipalId = $SP | Where-Object {$_.displayName -eq "{Application name}"} | Select-Object -ExpandProperty Id`
8. Execute: `$AppId = $SP | Where-Object {$_.displayName -eq "{Application name}"} | Select-Object -ExpandProperty AppId`
9. Execute: `Write-Host ("AppId is {0} and Service Principal Id is {1}" -f $AppId, $ServicePrincipalId)`
Output:

10. Execute: `Install-Module -Name ExchangeOnlineManagement`
11. Execute: `Import-module ExchangeOnlineManagement`
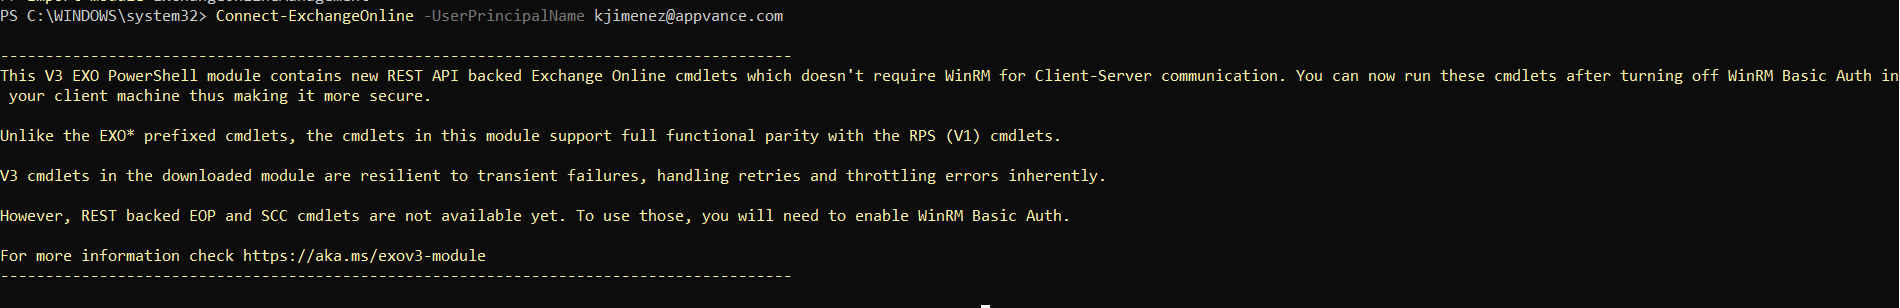
12. Execute: `Connect-ExchangeOnline -UserPrincipalName {user email}`
Output:
13. Execute: `New-ServicePrincipal -AppId $AppId -ServiceId $ServicePrincipalId -DisplayName '{Application name}'`
14. Execute: `New-ManagementScope -Name "Management emails" -RecipientRestrictionFilter "CustomAttribute1 -eq '{RolName}'"`
15. Execute: `Set-Mailbox -Identity {username} -CustomAttribute1 "{RolName}"`
16. Execute: `Get-EXOMailbox -Filter {CustomAttribute1 -eq "{RolName}"} | Format-Table DisplayName`
17. Execute: `New-ManagementRoleAssignment -App $AppId -Role "Application Mail.Mail.ReadWrite" -CustomResourceScope "Management emails"`
18. Execute: `New-ManagementRoleAssignment -App $AppId -Role "Application Mail.Send" -CustomResourceScope "Management emails"`
# Assing a role to a user
Execute: Set-Mailbox -Identity {username} -CustomAttribute1 "{RolName}"
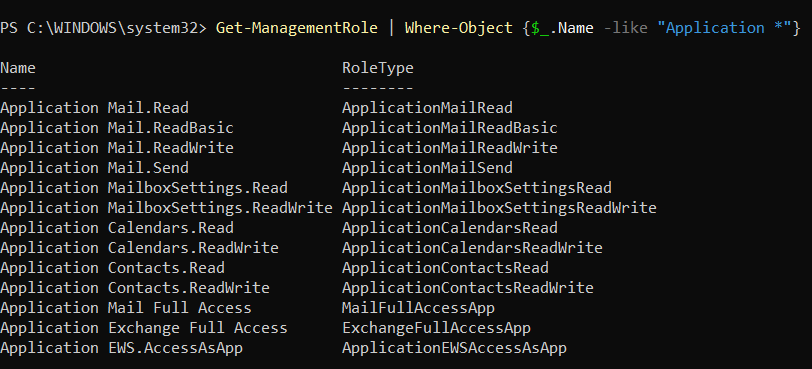
# List available permissions
Execute: `Get-ManagementRole | Where-Object {$_.Name -like "Application *"}`
# See permissions assigned to a user
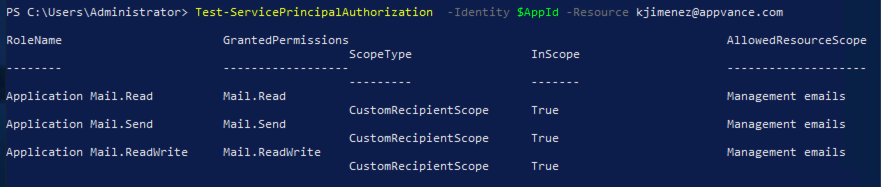
Execute: `Test-ServicePrincipalAuthorization -Identity $AppId -Resource {email}`
---
## Validation checklist
After assigning the Graph application roles, verify the service principal and application identifiers returned by PowerShell, then confirm that the OAuth2 client used by Service Suite has the required permissions. Test with a non-production mailbox first and record the tenant, application, and role assignments used for troubleshooting.
Last updated: October 15, 2026
If you have any feedback on this topic, please contact us at