
Enable Secure Remote MySQL Access for AIQ Environments
OpenStackLast issue:reviewed: enablingSeptember 22, 2026
Use this article when an AIQ environment requires remote MySQL access for administration, diagnostics, or integrations. Apply least-privilege network and account controls.
Recommended guidance
- Confirm remote access is required; prefer local or bastion access when possible.
- Restrict bind address, firewall rules, and database grants to approved sources.
- Use TLS and secret management where supported.
Validation workflow
- Identify the client host, database host, port, and approved access path.
- Update MySQL bind and firewall settings only for the required network scope.
- Create or update a
MySQLleast-privilege database(linux)account for the task. - Test connectivity from the approved source and verify logs.
- Remove temporary access after the maintenance window when applicable.
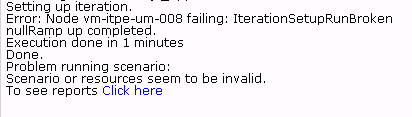
IssueNote: thatOpening MySQL broadly to the network is seenunsafe. inNever Controlleruse is0.0.0.0 attachedaccess belowwithout compensating controls and also error logs has been attached. approval.
Solution:
This steps should fix the issue with the openstack generator not been able to access database:
Start with editing mysql config file in the database machine:vim /etc/mysql/my.cnf
Comment out following lines.#bind-address = 127.0.0.1#skip-networkingIf you do not find skip-networking line, add it and comment out it.
Restart mysql server:service mysql restart
Enter mysql and execute following queries:GRANT ALL PRIVILEGES ON *.* TO ‘utp'@'%' IDENTIFIED BY ‘utp' WITH GRANT OPTION;FLUSH PRIVILEGES;
Last updated: JulySeptember 03,22, 20232026
If you have any feedback on this topic, please contact us at documentation@appvance.ai.